
Executive Summary
Hexastrike uncovered an undocumented commodity stealer and remote access toolset, which we track as FLEXRAT, distributed through counterfeit game-modification websites. The most prominent lure infrastructure impersonates the ecosystem surrounding ChilloutVR, a legitimate social VR platform, and advertises downloadable mods and plugins purported to extend the game’s functionality.
The campaign relies on search-driven delivery. Lure sites are positioned to capture users searching for terms such as “ChilloutVR Mods” and “ChilloutVR Plugins”, while their consistent design and game-themed domain names lend credibility with an audience already familiar with the platform. Download buttons deliver executables and archives hosted on Dropbox. Staging payloads on a widely trusted file-sharing service further lowers user suspicion and limits the effectiveness of reputation-based controls.
FLEXRAT is a multi-component ecosystem comprising Nim binaries, Go-based loaders, managed .NET components, and NSIS-packaged Electron applications. The Electron components carry the core capability set, spanning browser credential collection, Discord token theft, system reconnaissance, screenshot capture, persistence, and remote control.
Although the gaming-themed lure points primarily to consumer and prosumer victims, FLEXRAT’s capabilities are broadly comparable to those of contemporary commodity infostealers. Credentials and session data harvested from personal systems frequently extend to corporate accounts, giving the threat direct relevance for enterprise defenders. Historical mod-themed lure records reviewed during the investigation indicate the activity dates back to at least May 2026.
Key Findings
- FLEXRAT spreads through fake ChilloutVR game-mod and plugin lure sites promoted in search results, with the payloads staged on Dropbox to borrow the trust of a mainstream file-sharing service.
- The toolset is a commodity stealer and remote access trojan in one, built around an Electron application that hides an encrypted, obfuscated module bundle.
- It harvests browser credentials, cookies, and sessions along with Discord tokens and backup codes. Because those sessions and reused passwords often reach corporate accounts, any infection should be treated as a credential-exposure event.
- It establishes ASEP and scheduled task persistence after weakening UAC to elevate, masquerading as a Windows service and hiding its files with the hidden and system attributes.
- Command-and-control and exfiltration run over a small, reused set of FLEXRAT and L874 domains with Discord-based reporting, and the operator exposed its own code and project naming through embedded keys and a reused Discord webhook.
Targeting and Victimology
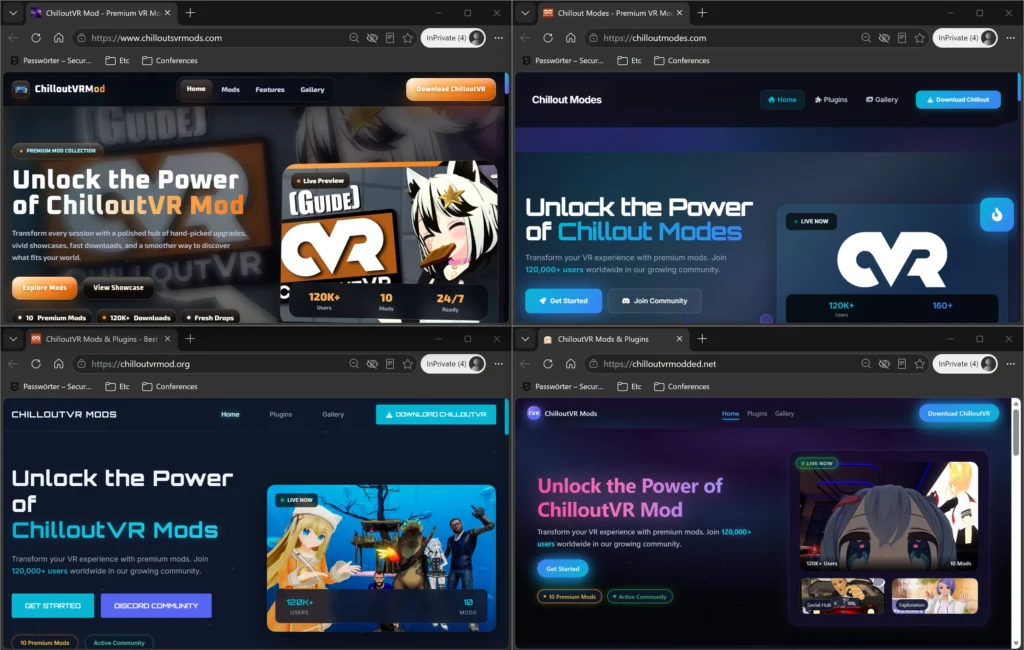
FLEXRAT distribution is opportunistic and aimed at users searching for ChilloutVR modifications and plugins. ChilloutVR is a legitimate social VR platform, and its branding is grafted onto unrelated malicious downloads to make them look relevant to the game and its community. The lure pages captured searches for terms such as “ChilloutVR Mods” and “ChilloutVR Plugins”, where they appeared alongside, and in some cases above, the legitimate results.

The lure domains are named around combinations of chillout, vr, mod, plugin, and spelling variations. Our investigation expanded to more than 100 hostnames spanning distribution candidates, related infrastructure, and contextual resources, hosted across the operator’s own domains as well as Netlify and Cloudflare Pages. The theme points at the ChilloutVR player community, but exposure is not limited to the game. Browser sessions and reused accounts recovered from personal systems frequently extend to accounts of higher value, which is what makes a consumer-facing lure an enterprise problem.
Infection Chain
Search Results, Mod Pages, and Dropbox Downloads
Entry occurs through game-mod search results and impersonating websites. The identified pages share a common presentation: consistent structure, game imagery, promotional copy, and prominent download buttons. They also link out to legitimate game and community resources, which adds familiar context around the malicious download.
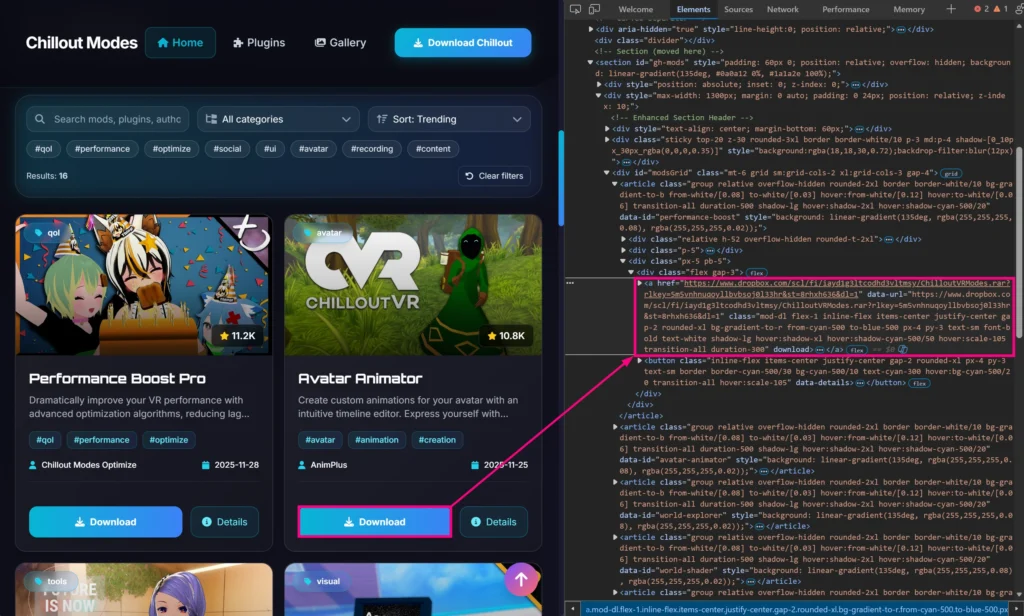
The advertised files are hosted on Dropbox, which separates the download location from the lure website. The links carry the dl=1 parameter to force a direct download rather than the Dropbox preview page.
NSIS Installer and Encrypted Electron Payload
The examined installer is an NSIS package containing an app-64.7z archive, which holds the Electron executable, resources\app.asar, and supporting files. Encryption is applied to the protected JavaScript bundle inside the application. The surrounding Electron package supplies the runtime and loader.
Electron reads the application’s package.json, whose main property selects electron-main.js. Once Electron signals readiness, electron-main.js loads the second-stage loader from compiled\index.js.

compiled\index.js.The wrapper writes diagnostic output to %USERPROFILE%\Desktop\debug_log.txt, falling back to C:\Users\Public\Desktop\debug_log.txt. When the compiled loader is missing, it sends a JSON report to https://flexrat.org/cdn/telemetry/error containing the hostname, a timestamp, and a missing-module message, authenticated with an embedded API key.

Protected containers follow a fixed layout: a 12-byte nonce, a 16-byte authentication tag, and AES-256-GCM ciphertext. The loader first reads compiled\data.res, decrypts it with the reconstructed 32-byte key 3400a2fdc62cefa8c0945b505dbff5540163ed30df84dd125bb64dcff6985600, and parses the resulting JSON manifest. It then Base64-decodes the selected manifest entry, decrypts it with the same key, and inflates the compressed JavaScript. A custom loader resolves relative imports, caches modules, and evaluates the recovered source, with the protected entry point selected through loadEncModule('index.js').

data.res decryption and module-loading routine.The recovered bundle comprises 33 modules covering browser collection, Discord collection, configuration, fleet control, and utilities, obfuscated with renamed identifiers, rotated string tables, and an additional string layer XORed with the repeating key KeshXRD. The recovered index.js coordinates collection, reporting, conditional persistence, and fleet startup.
Capabilities
The Electron modules carry out most actions through child processes launched via cmd.exe, usually with the console window hidden.
RAT and Command-and-Control Protocol
We recovered multiple FLEXRAT samples using different command-and-control and panel hosts: flexrat.org, flexrat.com, l874.xyz, and l874.lol. The same host serves both remote control and exfiltration. We assess with high confidence that L874 is the operator’s internal project name, based on the panel domains, the L874_ API key prefix, the l874_<milliseconds>.zip archive name, and the L874 PROJECT report footer. Each installation registers with the host, polls for commands, and returns results over dedicated routes carrying an embedded L874_ API key. The runtime configuration can redirect the client to a different host.

Operators can run shell commands, browse directories, transfer and launch files, capture screenshots, stream the screen, select monitors, control the mouse and keyboard, trigger text-to-speech and alerts, and lock the workstation. Collection reports are delivered as a Discord card footed L874 PROJECT | wolexasdas, with a button linking to https://l874.xyz and a hardcoded thumbnail at https://cdn.discordapp.com/attachments/1498687499898196039/1518406217729445948/image.png.
Browser and Credential Theft
The main entry point calls BrowserExtractor.extractDeep, which terminates running browsers before checking which profiles exist. It terminates chrome.exe, brave.exe, msedge.exe, opera.exe (Opera and Opera GX), vivaldi.exe, and browser.exe (Yandex and the conditional Comet build) with taskkill and verifies the termination with tasklist. This releases locked browser databases and produces a user-visible symptom: every browser closes at once shortly after the fake mod runs.
Chromium extraction then reads the browser databases and Local State keys and recovers protected material through DPAPI, app-bound-key handling, and token-impersonation attempts, using CreateFileW with shared access to read databases that other processes hold open. When direct extraction fails to return cookies, a Chrome DevTools Protocol fallback launches an installed Chrome, Brave, or Edge headless and off-screen, navigates to a fixed set of high-value sites (Discord, Google, YouTube, Amazon, and others), and calls Network.getAllCookies. A separate routine scrapes cookies from Network Service process memory.
Two Python helpers back the decryption paths: a Chromium helper that calls CryptUnprotectData, and a Firefox helper that decrypts through nss3.dll. Despite its source name decryptViaElevationService, the Chromium helper is a DPAPI fallback and not a browser elevation-service bypass.
Results are assembled into an in-memory ZIP uploaded as l874_<milliseconds>.zip. The archive is never written to disk:
l874_<milliseconds>.zip
├── system_info.txt
├── tokens.txt
├── backup_codes/
│   └── <email>_backup_codes.txt
└── browsers/
    ├── <browser>/<profile>/
    │   ├── pasavord.txt
    │   ├── cuckiee.txt
    │   └── aytofil.txt
    └── firefox/<profile>/
        ├── pasavord.txt
        └── cuckiee.txt
Discord Collection
Discord collection searches %APPDATA%\discord\Local Storage\leveldb and the discordcanary, discordptb, and discorddevelopment equivalents, LevelDB stores beneath the browser data roots, and Discord process memory. Candidate tokens are validated, deduplicated by account, and enriched with email and phone fields, MFA status, subscription and billing indicators, badges, and relationships. Backup-code collection searches the Downloads, Desktop, Documents, and profile-root folders for discord_backup_codes*.txt, selecting files whose contents include the account email.

System Reconnaissance
The system report includes the computer name, Windows edition and build, CPU, GPU, RAM, uptime, LAN IP, and antivirus indicators. OS and CPU values come from reg query, with a PowerShell Get-WmiObject Win32_VideoController fallback for the GPU. Security-product discovery runs tasklist /FO CSV /NH against process names for Microsoft Defender, Avast, AVG, Kaspersky, Norton, McAfee, Bitdefender, Malwarebytes, Sophos, Trend Micro, ESET, CrowdStrike, and SentinelOne, supplemented by install-directory checks.
Browser key recovery also drives a privileged-process lookup for lsass.exe, winlogon.exe, services.exe, and wininit.exe, whose PIDs feed DuplicateTokenEx-based token duplication and thread impersonation. Fleet registration identifies the device by the MachineGuid read from HKLM\SOFTWARE\Microsoft\Cryptography (lowercased, hyphens removed), falling back to xrd- followed by an MD5 of the hostname and username.
Screen Capture and Interactive Control
GDI and GDI+ routines capture the desktop, write %TEMP%\fleet_scr_<pid>.jpg, and upload it as screenshot.png alongside the collection archive. The same subsystem supports on-demand screen streaming, monitor selection, and remote mouse and keyboard control. FLEXRAT reaches the Windows API from JavaScript through Koffi, using CryptUnprotectData and NCryptOpenStorageProvider for credential recovery and the process and token APIs for enumeration, privilege adjustment, duplication, and impersonation.

%TEMP%\fleet_scr_<pid>.jpg before upload as screenshot.png.Anti-Analysis
The bundle contains an AntiSandbox utility that checks for an attached debugger, fewer than two processors, less than 2 GiB of RAM, VMware, VirtualBox, and Hyper-V adapter prefixes, and analysis process names including vboxservice, vmtoolsd, wireshark, fiddler, procmon, procexp, ollydbg, x64dbg, ida64, and httpdebugger.

AntiSandbox.isSandbox().We did not identify a caller for isSandbox across the 33 recovered modules, so the anti-analysis logic is present in the build but appears unreferenced in the analyzed sample. The bundle also contains a Stealth routine that patches its own PE subsystem and hides the console, and a SelfDestruct routine that deletes the executable or schedules deletion at reboot.
Persistence and UAC Weakening
Persistence runs after collection and reporting and is gated on an administrative token. The implant runs fltmc and treats success as proof of elevation. If it is not elevated, it relaunches itself through a hidden PowerShell Start-Process -Verb RunAs call carrying an --elevated marker. If the user declines the UAC prompt, the implant continues in a limited mode and installs no persistence. The branch is also skipped on an Electron or Node development execution or when it sees --restart.
Once elevated, the routine first weakens UAC, then establishes its persistent copy. It sets ConsentPromptBehaviorAdmin and PromptOnSecureDesktop to 0 beneath HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System, suppressing administrator consent prompts and the secure desktop for any remaining elevation. Because it modifies the prompt-behavior values rather than EnableLUA, the change takes effect immediately, without the reboot that disabling UAC outright would require.

ConsentPromptBehaviorAdmin and PromptOnSecureDesktop to 0.It then copies the running portable executable, located through the PORTABLE_EXECUTABLE_FILE environment variable set by electron-builder portable targets, to %ProgramData%\Microsoft\WindowsServiceHost\WindowsServiceHost.exe, and applies attrib +h +s to the file and its directory. The system attribute matters more than the hidden one, because Explorer conceals system-marked files even when “show hidden files” is enabled. When the portable executable cannot be located, the copy is skipped and persistence points to the current process.execPath without the hidden copy.
Startup is anchored two ways. The routine writes Windows Service Host values to the Run keys under both HKCU\Software\Microsoft\Windows\CurrentVersion\Run and HKLM\Software\Microsoft\Windows\CurrentVersion\Run, and it creates a scheduled task named WindowsServiceHost with an ONLOGON trigger and the highest run level.

WindowsServiceHost scheduled task configured for logon at the highest run level, alongside the Run values pointing to the persistent executable.Attribution
We do not attribute FLEXRAT to a named threat actor. We assess with moderate confidence that the developer is a Turkish speaker, based on language artifacts across multiple components. The recovered code contains Turkish-language logs and colloquial progress messages such as admin izni verildi knk (“admin permission granted, bro”), loglari gonderiyom (“sending the logs”), and LOG DÜŞTÜ (“log dropped”). A native configuration uses KULLANICIKEYI, meaning “user key”.
Two components retain paths under the Windows profile defen, including a OneDrive directory named Masaüstü, Turkish for Desktop:
C:\Users\defen\Desktop\xrddior\obj\Release\net8.0-windows\keshxrd.pdb
c:\Users\defen\OneDrive\Masaüstü\Project\Noface Project\bin\Release\net8.0-windows\SystemResourceProvider.dll
The managed loader also carries diagnostic source paths beneath /opt/Noface Project/, including Program.cs and modules/browsers/EngineCore.cs. Other internal labels include BrowserExtractor.Resources.xrd_engine.exe, Kateria - Owner Key, and L874 PROJECT | wolexasdas. The xrd naming recurs in the string-encoding key KeshXRD, the fallback device-ID prefix xrd-, and custom Discord emoji names.
Discord asset IDs bound the development of the reporting configuration to late April through late June 2026. The report-card assets were created on either side of the L874 domain registration on 15 June, with the final thumbnail uploaded one week later, which indicates the reporting configuration was finalized alongside the L874 infrastructure.
Detection Opportunities
-
Process lineage. Trusted applications rarely have a reason to spawn scripting engines or system utilities, and the parent–child relationship is usually the cleanest signal when they do. Node, PowerShell, Python, or VBScript spawned by an Electron application running from a user-writable path, especially when the child calls
fltmc,reg query, ortaskkill. -
Credential-theft precursors. Credential stores are usually tampered with before they are read, and that preparation is visible before any data is taken. Mass
taskkillagainst multiple browsers in quick succession, or a browser launched with remote-debugging or headless flags by a non-browser parent. -
Host and security-product reconnaissance. Malware profiles the host and its defenses before acting, and that fingerprinting usually runs through built-in tools that are easy to log. AV/EDR enumeration via
tasklist, machine-identifier reads from the registry, and token access to privileged system processes such aslsass.exeandwinlogon.exe. -
Security-policy changes. Security-relevant configuration should only change through managed deployment, so a write from anything else is suspicious regardless of the value set.
ConsentPromptBehaviorAdminorPromptOnSecureDesktopset to0by a non-management process. -
Masquerading persistence. Persistence that borrows the name of a legitimate component is betting that nobody checks the path and signer behind the name. Run values and scheduled tasks posing as a Windows service, and executables planted under
%ProgramData%. -
Attribute-based hiding. Payloads are often concealed with filesystem attributes rather than anything sophisticated, which keeps them out of casual inspection but leaves the act of hiding on record.
attrib +h +sapplied to files or folders underProgramData,AppData, orTemp, or on-disk files absent from a normal directory view. -
Outbound command-and-control. Whatever happens on the host, the results have to leave it, and egress to attacker infrastructure or abused legitimate services is the last reliable chokepoint. Connections to the domains listed below, or Discord webhook or CDN reporting from a non-browser process.
Hardening and Mitigation
-
Software delivery channels. Users should not be able to fetch and run executables from arbitrary internet sources, and narrowing where code can come from removes the initial access step for a whole class of campaigns. Flag or block direct executable and archive downloads from consumer file-sharing services at the proxy, including Dropbox direct-download links using the
dl=1parameter, and treat “game mod” or “plugin” installers from search results as high-risk. -
Application control. Code should only run from trusted, administrator-controlled locations, and anything written by the user or by a download should be denied by default. Use WDAC or AppLocker to block unsigned executables from user-writable paths such as
Downloads,AppData,ProgramData, andTemp, which breaks both the first-stage installer and the persistent copy. -
Privilege escalation controls. Elevation settings should not be modifiable by anything running in the user’s context, so enforce them centrally and deny the rights needed to change them locally. Enforce UAC through Group Policy (Behavior of the elevation prompt for administrators and Switch to the secure desktop when prompting for elevation) so writes to
ConsentPromptBehaviorAdminandPromptOnSecureDesktopare reverted on the next policy refresh, and keep daily-use accounts out of the local Administrators group so the malware never has the rights to write those values in the first place. -
Known malicious infrastructure. Blocking the operator’s command-and-control and reporting endpoints severs the implant from its controller and stops exfiltration even where execution has already occurred. Block or sinkhole the FLEXRAT and L874 domains and the lure hostnames listed below, and alert on outbound Discord webhook and CDN reporting originating from a non-browser process.
Conclusion
FLEXRAT is a capable commodity stealer and remote access toolset wrapped in a consumer-facing lure. The operator leans on SEO-driven delivery, impersonates the ChilloutVR modding ecosystem, and stages payloads on Dropbox so the download borrows the trust of a mainstream service. Behind the NSIS installer sits an Electron application with an encrypted, obfuscated 33-module bundle that performs broad browser and Discord credential theft, host reconnaissance, screenshot capture and screen streaming, UAC-weakening persistence, and full interactive remote control.
The lure aims at the ChilloutVR community, but the blast radius is wider. Browser sessions and reused passwords pulled from personal machines routinely unlock higher-value accounts, and unmanaged personal devices are a direct route into corporate environments. The operator’s reuse of a single embedded AES key, a shared Discord webhook, and recognizable development paths gave us the internal project naming and the full configuration, and it gives defenders durable indicators. Treat any FLEXRAT infection as a credential-exposure event and hunt the persistence and exfiltration chains described above.
MITRE ATT&CK Mapping
| Tactic | ID | Technique | FLEXRAT |
|---|---|---|---|
| Resource Development | T1583.001 | Acquire Infrastructure: Domains | Registered the FLEXRAT and L874 domains and dozens of chillout/vr/mod/plugin lure domains for lure hosting, reporting, and remote control. |
| Resource Development | T1583.006 | Acquire Infrastructure: Web Services | Lure sites were also hosted on Netlify and Cloudflare Pages. |
| Resource Development | T1608.001 | Stage Capabilities: Upload Malware | Installers and archives were staged on Dropbox using dl=1 direct-download share links. |
| Resource Development | T1608.006 | Stage Capabilities: SEO Poisoning | Lure pages were positioned to rank for “ChilloutVR Mods” and “ChilloutVR Plugins” searches. |
| Execution | T1204.002 | User Execution: Malicious File | Victims downloaded and ran fake ChilloutVR mod and plugin installers. |
| Execution | T1059.001 | Command and Scripting Interpreter: PowerShell | A PowerShell RunAs relaunch is used to obtain elevation. |
| Execution | T1106 | Native API | Koffi bindings call Windows APIs directly from JavaScript. |
| Persistence | T1547.001 | Boot or Logon Autostart Execution: Registry Run Keys | HKCU and HKLM Windows Service Host Run values point to the persistent executable. |
| Persistence | T1053.005 | Scheduled Task/Job: Scheduled Task | An ONLOGON WindowsServiceHost task runs the executable at the highest run level. |
| Privilege Escalation | T1548.002 | Abuse Elevation Control Mechanism: Bypass User Account Control | ConsentPromptBehaviorAdmin and PromptOnSecureDesktop are set to 0 and elevation is requested through RunAs. |
| Privilege Escalation | T1134.001 | Access Token Manipulation: Token Impersonation/Theft | DuplicateTokenEx and impersonation are used to recover protected credentials. |
| Defense Evasion | T1027 | Obfuscated Files or Information | JavaScript is obfuscated and strings are XOR-encoded with the key KeshXRD. |
| Defense Evasion | T1027.013 | Obfuscated Files or Information: Encrypted/Encoded File | Modules ship as AES-256-GCM encrypted containers (data.res and the module bundle). |
| Defense Evasion | T1140 | Deobfuscate/Decode Files or Information | The loader decrypts and inflates modules at runtime using an embedded AES key. |
| Defense Evasion | T1497.001 | Virtualization/Sandbox Evasion: System Checks | AntiSandbox checks CPU count, RAM, VM adapter prefixes, and analysis process names. |
| Defense Evasion | T1622 | Debugger Evasion | AntiSandbox checks for an attached debugger. |
| Defense Evasion | T1036.005 | Masquerading: Match Legitimate Name or Location | Persistence masquerades as Windows Service Host under %ProgramData%\Microsoft. |
| Defense Evasion | T1112 | Modify Registry | Run keys and UAC policy values are created or modified. |
| Defense Evasion | T1070.004 | Indicator Removal: File Deletion | A SelfDestruct routine deletes the executable or schedules deletion at reboot. |
| Credential Access | T1555.003 | Credentials from Password Stores: Credentials from Web Browsers | Passwords and autofill are extracted from Chromium browsers and Firefox. |
| Credential Access | T1539 | Steal Web Session Cookie | Cookies are extracted directly and via a Puppeteer/CDP fallback and process-memory scraping. |
| Credential Access | T1528 | Steal Application Access Token | Discord tokens are recovered, validated, and enriched. |
| Credential Access | T1552.001 | Unsecured Credentials: Credentials In Files | discord_backup_codes*.txt files are harvested when they match the account email. |
| Discovery | T1082 | System Information Discovery | Host inventory, OS build, hardware, uptime, and MachineGuid are collected. |
| Discovery | T1518.001 | Software Discovery: Security Software Discovery | The implant enumerates installed antivirus and EDR products. |
| Discovery | T1057 | Process Discovery | Running processes are enumerated for analysis-tool and token checks. |
| Collection | T1113 | Screen Capture | The desktop is captured through GDI/GDI+ and streamed on demand. |
| Collection | T1560 | Archive Collected Data | Stolen data is assembled into an in-memory ZIP (l874_<ms>.zip). |
| Command and Control | T1071.001 | Application Layer Protocol: Web Protocols | Registration, polling, and result delivery use HTTPS to FLEXRAT hosts. |
| Command and Control | T1102 | Web Service | Discord (webhook and CDN) is used for reporting and card delivery. |
| Command and Control | T1573.002 | Encrypted Channel: Asymmetric Cryptography | C2 traffic is carried over HTTPS/TLS. |
| Exfiltration | T1567 | Exfiltration Over Web Service | The native and managed components deliver collection reports through a Discord webhook. |
| Exfiltration | T1041 | Exfiltration Over C2 Channel | The Electron component uploads the stolen-data archive and screenshot over its registration and result routes. |
Indicators of Compromise
| Category | Type | Value | Comment | First Seen | Last Seen |
|---|---|---|---|---|---|
| Network activity | domain | flexrat.org | Electron reporting and remote-control host | – | – |
| Network activity | domain | flexrat.com | Managed component engine-delivery host | – | – |
| Network activity | domain | l874.xyz | Panel URL in the decrypted Electron configuration | – | – |
| Network activity | domain | l874.lol | Contacted by a related Go artifact | – | – |
| Network activity | URL | https://cdn.discordapp.com/attachments/1498687499898196039/1518406217729445948/image.png | Hardcoded report-card thumbnail | 2026-06-22 | – |
| Lure infrastructure | domain | chilloutmod.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutmod.pages.dev | ChilloutVR-themed lure hostname (Cloudflare Pages) | – | – |
| Lure infrastructure | domain | chilloutmode.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutmodes.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutmods.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutmods.pages.dev | ChilloutVR-themed lure hostname (Cloudflare Pages) | – | – |
| Lure infrastructure | domain | chilloutmodsvr.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutmodsvr.pages.dev | ChilloutVR-themed lure hostname (Cloudflare Pages) | – | – |
| Lure infrastructure | domain | chilloutmodvr.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutmodvr.info | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutmodvr.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutmodvr.online | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutmodvrr.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutplugin.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutplugins.info | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutplugins.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutsmods.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrmod.com | Retained a FlexRat Secure Platform page title; apex hosted ChilloutVR-themed content | – | – |
| Lure infrastructure | domain | chilloutsvrmod.com.tr | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrmod.info | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrmod.online | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrmods.com | Linked to the Dropbox download Vrmod_Setup.exe | – | – |
| Lure infrastructure | domain | chilloutsvrmods.com.tr | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrmods.info | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrmods.online | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutsvrworld.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvr-docs.pages.dev | ChilloutVR-themed lure hostname (Cloudflare Pages) | – | – |
| Lure infrastructure | domain | chilloutvr-mods.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutvr-x.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutvr.cc | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvr.info | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvr.online | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvr.org | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvr.vip | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrbeta.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutvrchat.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrgame.net | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrhub.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrlabs.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrlabs.com.tr | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrlabs.info | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrlabs.online | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmod.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmod.net | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmod.org | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmod.vip | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmodded.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmodded.net | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmods.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmods.net | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrmods.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutvrmods.netliy.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | chilloutvrmods.pages.dev | ChilloutVR-themed lure hostname (Cloudflare Pages) | – | – |
| Lure infrastructure | domain | chilloutvrmods.xyz | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrplugin-d6v.pages.dev | ChilloutVR-themed lure hostname (Cloudflare Pages) | – | – |
| Lure infrastructure | domain | chilloutvrplugin.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrplugin.xyz | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrplugins.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrsmod.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutvrsmod.net | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chilloutworlds.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chillvrmod.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | chillvrmod.online | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | customvrchat.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | lexoramods.com | Related lure hostname | – | – |
| Lure infrastructure | domain | modschillout.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | modschilloutvr.com | ChilloutVR-themed lure hostname | – | – |
| Lure infrastructure | domain | modschilloutvr.netlify.app | ChilloutVR-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | qabyostore.icu | Related lure hostname | – | – |
| Lure infrastructure | domain | vrchatmod.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | vrchatmodes.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | vrchatsmod.netlify.app | VRChat-themed lure hostname (Netlify) | – | – |
| Lure infrastructure | domain | vrchilloutmod.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | vrchilloutmods.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | vrchilloutmods.shop | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | vrcplugin.com | VRChat-themed lure hostname | – | – |
| Lure infrastructure | domain | vrcpluginlab.com | VRChat-themed lure hostname | – | – |
| Payload staging | URL | http://www.dropbox.com/scl/fi/58zjwuoe83qjjpj7tt3y2/ChilloutVrMod.exe?rlkey=vojb0l0ls4uc32z51ykogot24&st=wftymyy8&dl=1/ | Dropbox-hosted ChilloutVrMod.exe (plain-HTTP variant) | – | – |
| Payload staging | URL | http://www.dropbox.com/scl/fi/7hp56yj650o4slrllg4xj/ChilloutVRMod.exe?rlkey=s69vdpczdpalbo26alwo0u13o&st=f5mgwsxk&dl=1/ | Dropbox-hosted ChilloutVRMod.exe (plain-HTTP variant) | – | – |
| Payload staging | URL | http://www.dropbox.com/scl/fi/ltfvmwrjb1muy5evusjqp/Chillout-VR-Mods.zip?rlkey=cyjdi4lu89o3asio0u2why0fj&st=evbv1apd&dl=1/ | Dropbox-hosted Chillout-VR-Mods.zip (plain-HTTP variant) | – | – |
| Payload staging | URL | http://www.dropbox.com/scl/fi/otfakqkze127a701il1zh/Vrmod_Setup.exe?rlkey=deryztzard7w3n2btuqo7ivvd&st=48dlc6qm&dl=1/ | Dropbox-hosted Vrmod_Setup.exe (plain-HTTP variant) | – | – |
| Payload staging | URL | http://www.dropbox.com/scl/fi/otfakqkze127a701il1zh/vrmod_setup.exe?rlkey=deryztzard7w3n2btuqo7ivvd&st=48dlc6qm&dl=1 | Dropbox-hosted vrmod_setup.exe (plain-HTTP variant) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/0rsrugbxi70u1ntgisp1a/ChilloutVRMods-Setup-2.1.1.exe?rlkey=16j52y2an1hi8eb5wdi86wtz3&st=p548et18&dl=1 | Dropbox-hosted ChilloutVRMods-Setup-2.1.1.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/19n7l1ifh5ha1x8uvlexy/ChilloutVrMod.exe?rlkey=s3452vgfp5c4y3nyh86jw58ta&st=psibftcq&dl=1 | Dropbox-hosted ChilloutVrMod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/22cucp9cvcjrru5qwe5u5/ChilloutVrMod.exe?rlkey=79jxu4d516slqydk1prnaty1g&st=hj68h82r&e=1&dl=1 | Dropbox-hosted ChilloutVrMod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/34l5x9j2znapj1h70c97m/vrmod_Setup.rar?rlkey=ckpqaffuowlxfb8p1h1tq9qqr&st=2vsrjdxt&dl=1 | Dropbox-hosted vrmod_Setup.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/3ah7he0pwamjoiizt1pwi/VrModSetup.rar?rlkey=9oiv5cl1hqolbu21i7ofgmvis&st=jiluycdz&dl=1 | Dropbox-hosted VrModSetup.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/3vhl2f0sypdk2vmobxfw0/ChilloutVrMod.exe?rlkey=h47ewl6fmdcu8t32s0hfpsgag | Dropbox-hosted ChilloutVrMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/3vhl2f0sypdk2vmobxfw0/ChilloutVrMod.exe?rlkey=h47ewl6fmdcu8t32s0hfpsgag&st=ism1w2l7&dl=1 | Dropbox-hosted ChilloutVrMod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/4rzlfjr4cs5e0n5wywkpo/VrChatPlugins.exe?rlkey=bedi2i8r7i7d1m1sgfxx7xen1&st=h7irzr5p&dl=1 | Dropbox-hosted VrChatPlugins.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/543sq91b5qgpknm3g9slg/ChillOut_ERP_MODS.zip?rlkey=cxb2jdeegeqkm49tuzhzhjr02&st=qo4ht01o&dl=1 | Dropbox-hosted ChillOut_ERP_MODS.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/58zjwuoe83qjjpj7tt3y2/ChilloutVrMod.exe?rlkey=vojb0l0ls4uc32z51ykogot24 | Dropbox-hosted ChilloutVrMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/58zjwuoe83qjjpj7tt3y2/ChilloutVrMod.exe?rlkey=vojb0l0ls4uc32z51ykogot24&st=wftymyy8&dl=1 | Dropbox-hosted ChilloutVrMod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/5toc5n7dn6iuvuz2mnchv/ChilloutVR-Installer.exe?rlkey=ug71wqmu1zqo4hq01zj9b9fv3&st=wa0eztb1&dl=1 | Dropbox-hosted ChilloutVR-Installer.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/5ymo1rxegi5o6tu05wxrb/ChilloutVrMod.exe?rlkey=euxl088xf9f95bbx96n55kawn&st=49bj3gx6&dl=1 | Dropbox-hosted ChilloutVrMod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/7hp56yj650o4slrllg4xj/ChilloutVRMod.exe?rlkey=s69vdpczdpalbo26alwo0u13o | Dropbox-hosted ChilloutVRMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/7hp56yj650o4slrllg4xj/ChilloutVRMod.exe?rlkey=s69vdpczdpalbo26alwo0u13o&st=f5mgwsxk&dl=1 | Dropbox-hosted ChilloutVRMod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/7urmetleawb4xtkp7rge8/Chilloutvrmod_64x.exe?rlkey=4etnrbmze203qbzeh3vcyh8ze&st=zuxgaweu&dl=0 | Dropbox-hosted Chilloutvrmod_64x.exe (preview-link variant) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/8ragf48gfd17vm23ml5rs/ChilloutsMod_setup64x.exe?rlkey=cklolpt816bgsbypybpnigaw7&st=mewr39bk&dl=1 | Dropbox-hosted ChilloutsMod_setup64x.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/8x27d1a8hdsltqiajbi5e/vrmod.rar?rlkey=ah50utzt2h6h3dizzsy4ekhu2&st=u8mh2nk7&dl=1 | Dropbox-hosted vrmod.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/9akfq9btu14j44xvaxvhg/ModLoader.exe?rlkey=yooih1ki5b7tkp5ntn510x9l0&st=vivum88k&dl=1 | Dropbox-hosted ModLoader.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/9vkf3xq0pru0zrsmar2ul/ChilloutvrMods.exe?rlkey=pe6tb6dzne2lsubn1eqaynplh&st=qdmp1iwl&dl=1 | Dropbox-hosted ChilloutvrMods.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/abwqmzzpzaojx8cj7fxb5/ChilloutVRChatModSetup.exe?rlkey=m1h0d1opjgc07ik3m6ybr85vs&st=t96q5dzu&dl=0 | Dropbox-hosted ChilloutVRChatModSetup.exe (preview-link variant) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/abwqmzzpzaojx8cj7fxb5/ChilloutVRChatModSetup.exe?rlkey=m1h0d1opjgc07ik3m6ybr85vs&st=t96q5dzu&dl=1 | Dropbox-hosted ChilloutVRChatModSetup.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/bgi9suvtpdj23y8l51sja/ChilloutVrMod.exe?rlkey=qtsfve7cajo5vzaml8ncupsxc | Dropbox-hosted ChilloutVrMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/c1q48qu0esrkjjwf1kcrg/ChilloutVR.zip?rlkey=cwe2zoas823xn6grh0k9ylhpc&st=hth79qst&dl=1 | Dropbox-hosted ChilloutVR.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ca2ddo6roivd7060srbhe/ChilloutsvrMod.exe?rlkey=g799cifuovjggjd70cn9o70zd | Dropbox-hosted ChilloutsvrMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/cpi960q07wn3trngfe53w/ChilloutVrMod.exe?rlkey=xqkojk8nzlnw848akh5s976vd | Dropbox-hosted ChilloutVrMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/dcdivjf5ghqnskqv7hngd/ChilloutVRMods.zip?rlkey=l4i3culfodilw946ulcgj0ptd&st=zr8dzwkr&dl=1 | Dropbox-hosted ChilloutVRMods.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/dtdxb7ilb2gze0dn5ynhe/ChilloutVR-X62.exe?rlkey=daiey8lzb1guttjfwp5i3k292&st=g83wkhb2&dl=1 | Dropbox-hosted ChilloutVR-X62.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/dtxmx0ihc24pvye2455qs/Chillout-Mod.exe?rlkey=la93pvxgebla6k7fakqhawpdm&st=6qpk64m9&dl=1 | Dropbox-hosted Chillout-Mod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ehjtlctugd0vi8oj0to13/ChilloutVR-Mod.exe?rlkey=vg744rmwuuu7zstv7mifwo1y8 | Dropbox-hosted ChilloutVR-Mod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ehjtlctugd0vi8oj0to13/ChilloutVR-Mod.exe?rlkey=vg744rmwuuu7zstv7mifwo1y8&st=euc4cai5&dl=1 | Dropbox-hosted ChilloutVR-Mod.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/fo6xuu068sa1j8wskbplc/ChilloutVRMods.zip?rlkey=nvff1mifs3egerkcmxs8z9pc4 | Dropbox-hosted ChilloutVRMods.zip (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/h6nks7mkbfhshdk7w35kz/ChilloutVRMods-Setup-2.1.1.exe?rlkey=610ltlk8flhox71mptamus2pf&st=6vg26kni&dl=1 | Dropbox-hosted ChilloutVRMods-Setup-2.1.1.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/hv9kv2cvu7wibxe9z1hcq/ChillOutVrMods.exe?rlkey=533x4mpvz2ha4be7z0l67i4wy&st=28ti4xn3&dl=1 | Dropbox-hosted ChillOutVrMods.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/iayd1g3ltcodhd3vltmsy/ChilloutVRModes.rar?rlkey=5m5vnhnuqoyllbvbsoj0l33hr&st=8rhxh636&dl=1 | Dropbox-hosted ChilloutVRModes.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/iu1ejfkp6u8bjuvcfidhu/CustomVR-Setup-3.78.4.exe?rlkey=qlqa1zv6dopc37bdo97cshjlt&st=hoh2sgkn&dl=1 | Dropbox-hosted CustomVR-Setup-3.78.4.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/izlwnwd4ub5upnc5e790c/ChilloutVRMods-x64.exe?rlkey=y0jz1zgqh4tc7lpjzzjmzz8an&st=6lpl54tu&dl=1 | Dropbox-hosted ChilloutVRMods-x64.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/kkdrv5ln4yizke94qbsd4/VrChatModes.rar?rlkey=lw23cwt3828plnfkmn9zzej36&st=i32sk2m7&dl=1 | Dropbox-hosted VrChatModes.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/l4hpmsy11ygjhx6mo8624/ChilloutVRSetup.zip?rlkey=gthc8o6plgt8eef7319n7gzn2&st=3r1tm9b6&dl=1 | Dropbox-hosted ChilloutVRSetup.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/lp7q1mv51pl6vdsrox7lt/chilloutvr_mods_setup64x.exe?rlkey=qgmfarkuzyhyqhjutfl7twz37&st=pb5wnset&dl=1 | Dropbox-hosted chilloutvr_mods_setup64x.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/lq55bq5k4fhpzbt25l74d/chilloutvrmod.rar?rlkey=iifhths8wl25fqjem1stlodbo&st=ur88pvoy&dl=1 | Dropbox-hosted chilloutvrmod.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ltfvmwrjb1muy5evusjqp/Chillout-VR-Mods.zip?rlkey=cyjdi4lu89o3asio0u2why0fj | Dropbox-hosted Chillout-VR-Mods.zip (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ltfvmwrjb1muy5evusjqp/Chillout-VR-Mods.zip?rlkey=cyjdi4lu89o3asio0u2why0fj&st=evbv1apd&dl=1 | Dropbox-hosted Chillout-VR-Mods.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/mdnrgswbk6pc6vihqtvi9/ChilloutVRMods.zip?rlkey=njuhe53zdgyp3tzpjv5urfoit&st=zkm8uznd&dl=1 | Dropbox-hosted ChilloutVRMods.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ml391r3zzafglnslug3tl/Vrmod_Setup.rar?rlkey=km7efhe8g7hqfjwjgvodtpw25&st=k42n9qy7&dl=1 | Dropbox-hosted Vrmod_Setup.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/mqy9e43vm3xve3oeiw4nu/VrChatMods-Setup-1.0.0.exe?rlkey=2720fycjl5t2enl0fgamoksxd&st=lc8crejc&dl=1 | Dropbox-hosted VrChatMods-Setup-1.0.0.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/my83eu1qh0raay1f4ir7w/ChilloutVR-ChatMod.7z?rlkey=s5lc7xukrzkils2qubx6ymluy&st=edvlph6h&dl=1 | Dropbox-hosted ChilloutVR-ChatMod.7z | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/nolk72zd5c719i0dag7gn/ChilloutVRMod.exe?rlkey=ftkccofc8mkgfhx270dp2hi5n | Dropbox-hosted ChilloutVRMod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ns0cy91r5q4eekwut9tbv/ChilloutMods_Setup64x.exe?rlkey=ra0y8p22e5cvcjhk3ai1410ow&st=ukb7har2&dl=1 | Dropbox-hosted ChilloutMods_Setup64x.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ns0cy91r5q4eekwut9tbv/ChilloutMods_setup64x.exe?rlkey=ra0y8p22e5cvcjhk3ai1410ow&st=0tesl0ga&dl=1 | Dropbox-hosted ChilloutMods_setup64x.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/ns0cy91r5q4eekwut9tbv/ChilloutMods_setup64x.exe?rlkey=ra0y8p22e5cvcjhk3ai1410ow&st=3sj37sd6&dl=1 | Dropbox-hosted ChilloutMods_setup64x.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/nskicttnk1gpvzl0uhrl3/VrChatPlugins.exe?rlkey=39fy70x9tzlkkeafa4oev0vm3&st=z2ewidgv&dl=1 | Dropbox-hosted VrChatPlugins.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/nuecx0f1co2p615wbrt1k/ChilloutVR-ModManager.exe?rlkey=vbab0thmbid79pkvtl5va1rxw&st=pv44yyzx&dl=1 | Dropbox-hosted ChilloutVR-ModManager.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/nwo9vhdklyxsfblkp1ws5/ChilloutPlugins.zip?rlkey=h4oscctk9xm4b8j7976a4aej2 | Dropbox-hosted ChilloutPlugins.zip (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/otfakqkze127a701il1zh/Vrmod_Setup.exe?rlkey=deryztzard7w3n2btuqo7ivvd | Dropbox-hosted Vrmod_Setup.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/otfakqkze127a701il1zh/Vrmod_Setup.exe?rlkey=deryztzard7w3n2btuqo7ivvd&st=48dlc6qm&dl=1 | Dropbox-hosted Vrmod_Setup.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/oylnrqzho0a95nwrfq0kp/ChilloutModPack.rar?rlkey=tc9iu840j5n4rk4pnc465twmg&st=wnop3egj&dl=1 | Dropbox-hosted ChilloutModPack.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/pjq11z38imwuarxmnamwi/ChilloutMods_setup64x.exe?rlkey=cx8nv5x4s830w7istwjtgcniz&e=1&st=waxs0wz4&dl=1 | Dropbox-hosted ChilloutMods_setup64x.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/qm0tfghcfyx83k87om441/chilloutvrmod.rar?rlkey=yarmvsh7zgt4n1hm2114k6ksw&st=weirfjbt&dl=1 | Dropbox-hosted chilloutvrmod.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/reu4jfk9kcwsemndcp17u/ChilloutVrMods.zip?rlkey=dt3s5t7cm6g2jrtu6fp041iw6&st=j2d888o6&dl=1 | Dropbox-hosted ChilloutVrMods.zip | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/sc4cewcph73x6my6i2btq/Plugins.rar?rlkey=xd21ovc3opifve2snjyjn559h&st=rlghroly&dl=1 | Dropbox-hosted Plugins.rar | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/snh9ge3iws7s63rdfraqa/Chillout-VR-Mod.exe?rlkey=gxi36a9jtre43gzs2d08npsu3 | Dropbox-hosted Chillout-VR-Mod.exe (share link without dl parameter) | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/tcgv7hnv82ozxb6zsb8u8/ChilloutVR-Latest.exe?rlkey=lw8xl821mboa0zg2dwmtn1p5t&st=62jbcev6&dl=1 | Dropbox-hosted ChilloutVR-Latest.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/wc0si9kji4f0lty0dbxey/chiloutvrmod_Setup.exe?rlkey=s7877eynqsa1oe339f6zsiybe&e=1&st=t78inqag&dl=1 | Dropbox-hosted chiloutvrmod_Setup.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/xwp3q2qsvvagwixixi5lp/ChilloutModSetup.exe?rlkey=e8ehsruyafg87tnl0pd6yxi2a&st=oihbjf9q&dl=1 | Dropbox-hosted ChilloutModSetup.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/yvh12d9y2u2ryvkbfnebx/ChilloutGameSetup.exe?rlkey=mum6xl3fisrm6ylwa2chzaokv&st=wgtfrnqe&dl=1 | Dropbox-hosted ChilloutGameSetup.exe | – | – |
| Payload staging | URL | https://www.dropbox.com/scl/fi/zwhuxivijjxp6aeg2jo0n/ChillOutVRModsInstaller.zip?rlkey=4vwm0e516iq4v28q5axs7syum&st=rjveoux7&dl=1 | Dropbox-hosted ChillOutVRModsInstaller.zip | – | – |
